Attackers Love Cookies: Tracing the Rise of Breaches Involving Session Cookie Theft
In this article, we explore the growing threat trend of breaches involving stolen session cookies, examining the factors driving this type of attack, their impact, and the defenses enterprises can implement to prevent them.
Hybrid work has changed system administration
Today, system administration rarely happens from fixed workstations behind a corporate perimeter. According to HP’s 2025 Work Relationship Index, one in five employees now work flexibly across office, home and mobile environments.[1] At the same time, many enterprises have moved their core infrastructure to the cloud. Microsoft Entra and similar platforms have replaced on-premise domain controllers, eliminating VPN and RDP sessions in favor of management using a web browser.
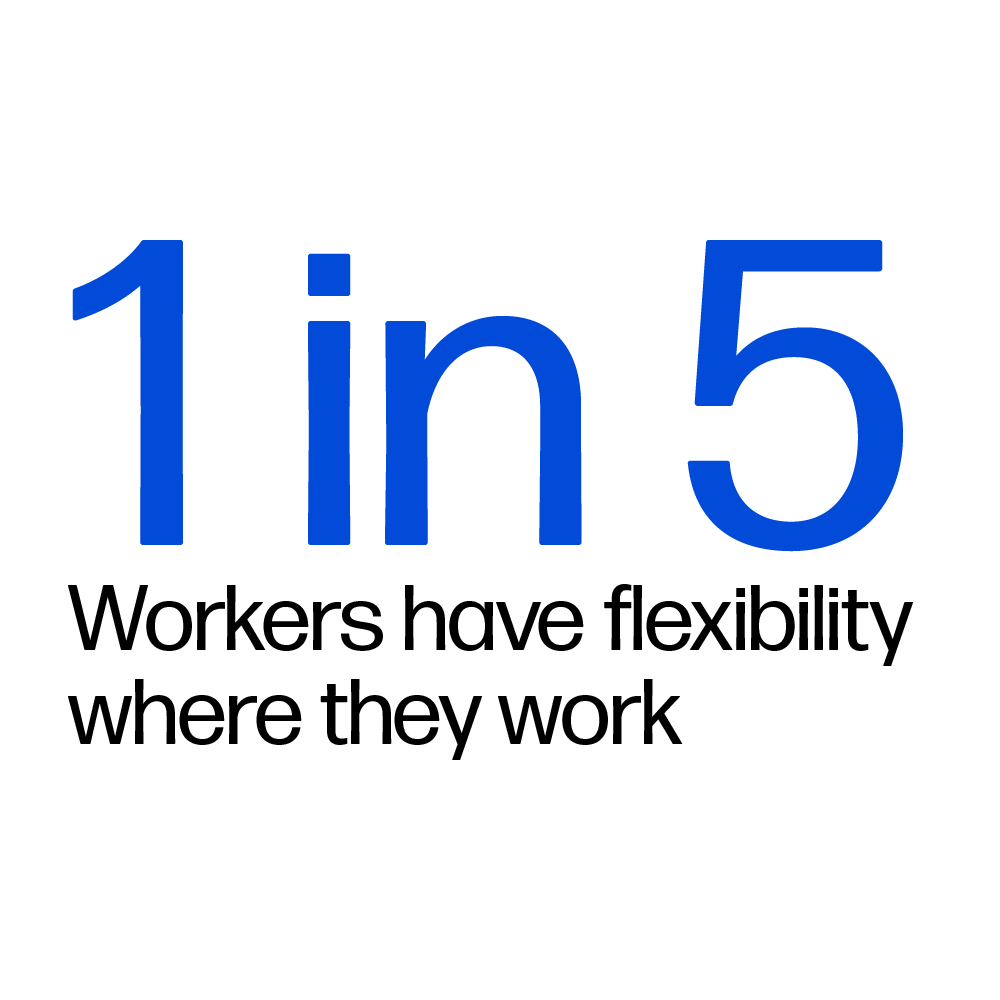
Previously, company networks were usually administered from workstations remoting to servers like domain controllers. This way, system administrators managed users and computers, defined and edited Group Policies and administered email and DNS servers. Most of the relevant servers were in the same network, and protected against external attacks by a perimeter, akin to a castle and moat.
But if an attacker were able to penetrate the network, they could move laterally and ultimately compromise critical servers like a domain controller, taking control of the network. In response to this risk, Microsoft introduced a tiering model as best practice for administering critical servers that involves logically separating the administrative levels of IT systems. The standard way of implementing this is by using two devices: a privileged access workstation (PAW) for important administration tasks and a separate device for everything else. This minimizes the attack surface and reduces an attacker’s opportunities for lateral movement in a compromised environment.
In contrast, administration using web browsers is now far more convenient for system administrators. But this move to the browser hasn’t eliminated the need to separate administrative levels. Other security measures like using passwordless authentication and multi-factor authentication (MFA) are helpful, but ultimately aren’t a replacement for strong privilege separation.
On the attack side, we’re seeing a change in the way that threat actors breach organizations. Rather than steal credentials, attackers are now increasingly focusing on stealing authentication cookies. In this type of attack, a threat actor no longer needs to steal credentials or bypass MFA. Instead, they simply need the browser cookie that proves the target user (e.g. a system administrator) is logged in. Once they have it, they effectively have the privileges and access of that user.
Where defenders understand these threats, for example in critical infrastructure sectors, there’s growing demand for strong technical solutions like PAWs. At the same time, developing regulatory requirements are introducing controls that enforce best-practice security measures, often requiring separate devices for secure remote system administration. This is creating a rising tension between cost, security and usability – a trade off that will likely grow as this threat trend develops.
Credential theft is popular but preventable with MFA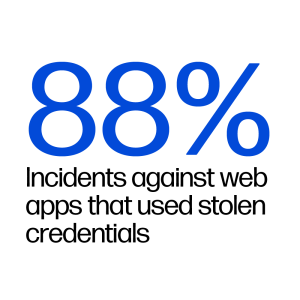
Two common ways threat actors obtain credentials are through theft (e.g. phishing) or guessing (e.g. in a brute-force attack). Attackers carry out targeted and well-crafted phishing campaigns to obtain login information. This information is then sold on hacking marketplaces or used to gain unauthorized access to a wide variety of systems. Many of these credentials can be purchased cheaply by other threat actors, meaning the skills and resources to gain initial access to systems is alarmingly low.
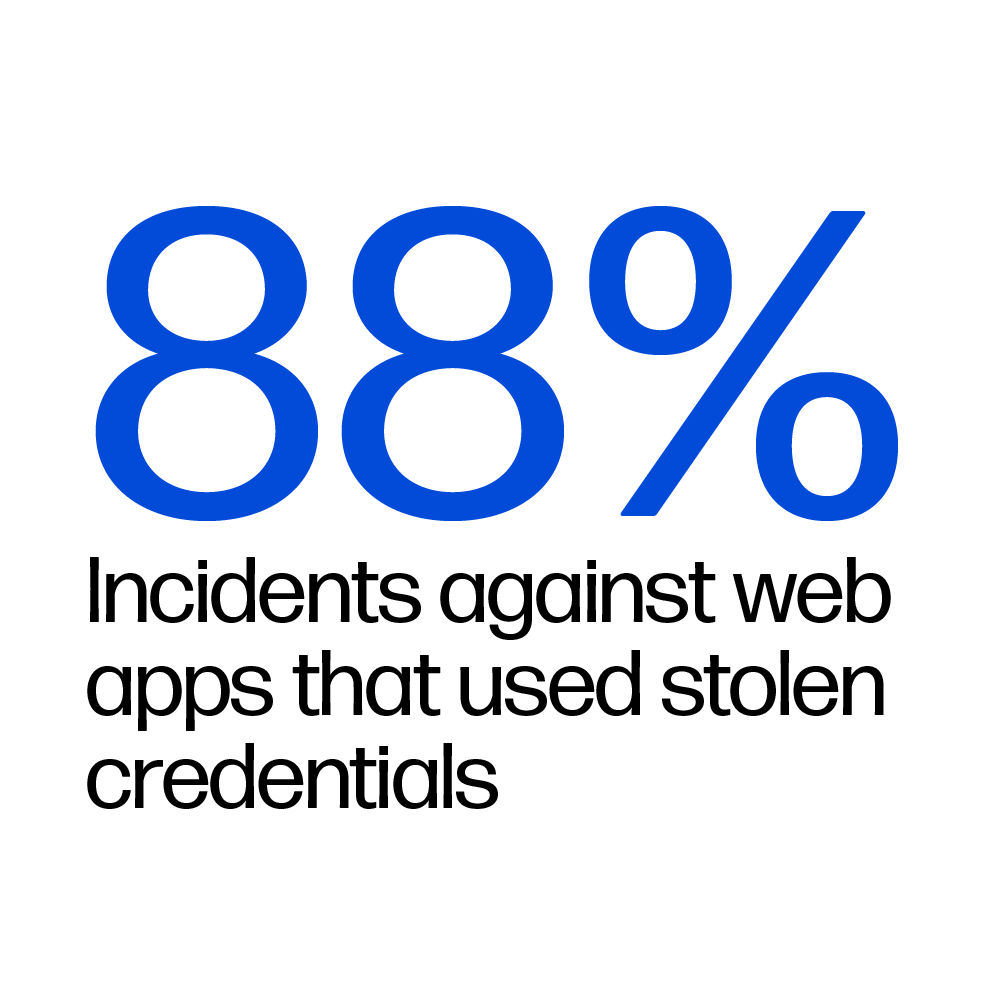
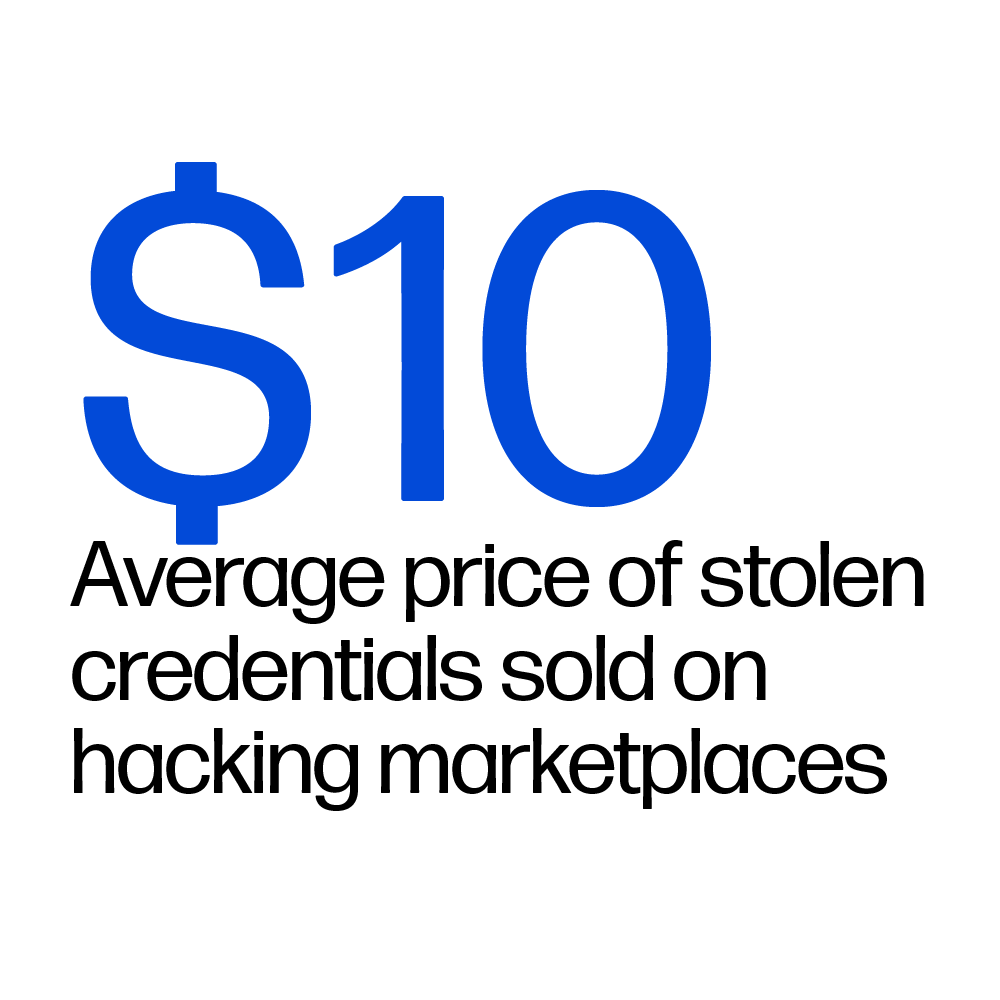
Stolen credentials are popular among attackers. They were used in 88% of incidents against web applications (e.g. online banking and system management tools), according to Verizon’s 2025 Data Breach Investigation Report.[2] Every day, thousands of stolen credentials are advertised on hacking marketplaces and sold for $10 USD on average.[3]
In certain cases, this may be the last step in a compromise, but in others, it may simply be the first in a larger and more complex network intrusion.
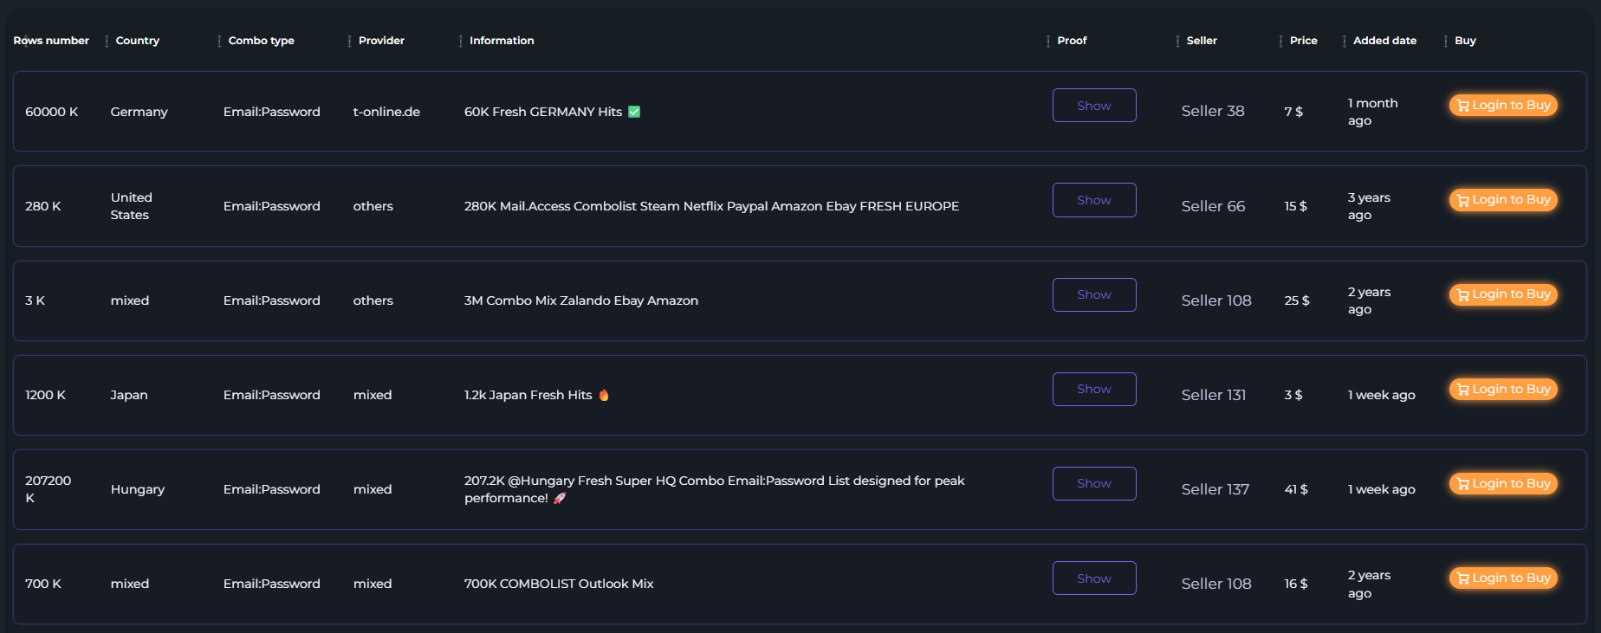
Figure 1 – Hacking marketplace advertising stolen credentials
 An effective defense against credential theft is MFA. This means that authentication usually takes place in two steps. First, you need valid credentials to login, such as your username and password, but in addition to this you also need a configured second factor. The second factor can take many forms, with the most common being time-based one-time passwords, SMS codes, mobile phone push notification approvals, hardware security keys, or email confirmations.
Since attackers should not have access to this second factor, they are unable to gain unauthorized access to a system even when login credentials have been compromised. However, MFA isn’t a silver bullet because it doesn’t protect against stolen session cookie attacks.
The danger of stolen session cookies and tokens
Each time a user logs into a system, an authentication session is opened for that user. This session is used to maintain an active login when interacting with the system. Various methods can be used to store an open authentication session on the client. The session can, for example, be stored locally on the user’s device in localStorage, sessionStorage or as a cookie. Storing the active session in the form of a cookie is standard practice and is used by most web applications. This is because cookies are automatically sent to the server with every HTTP request, eliminating the need for manual session management.
If an attacker can obtain the authentication cookie, they can take over the active session and gain unauthorized access to a system. This gives the attacker the same access to the system as the initial user. So, if the user is a Microsoft Entra administrator, the attacker can gain critical permissions to an entire organization. In such a case, the attacker could weaken or bypass security controls, gain elevated privileges, or set up a persistent backdoor.
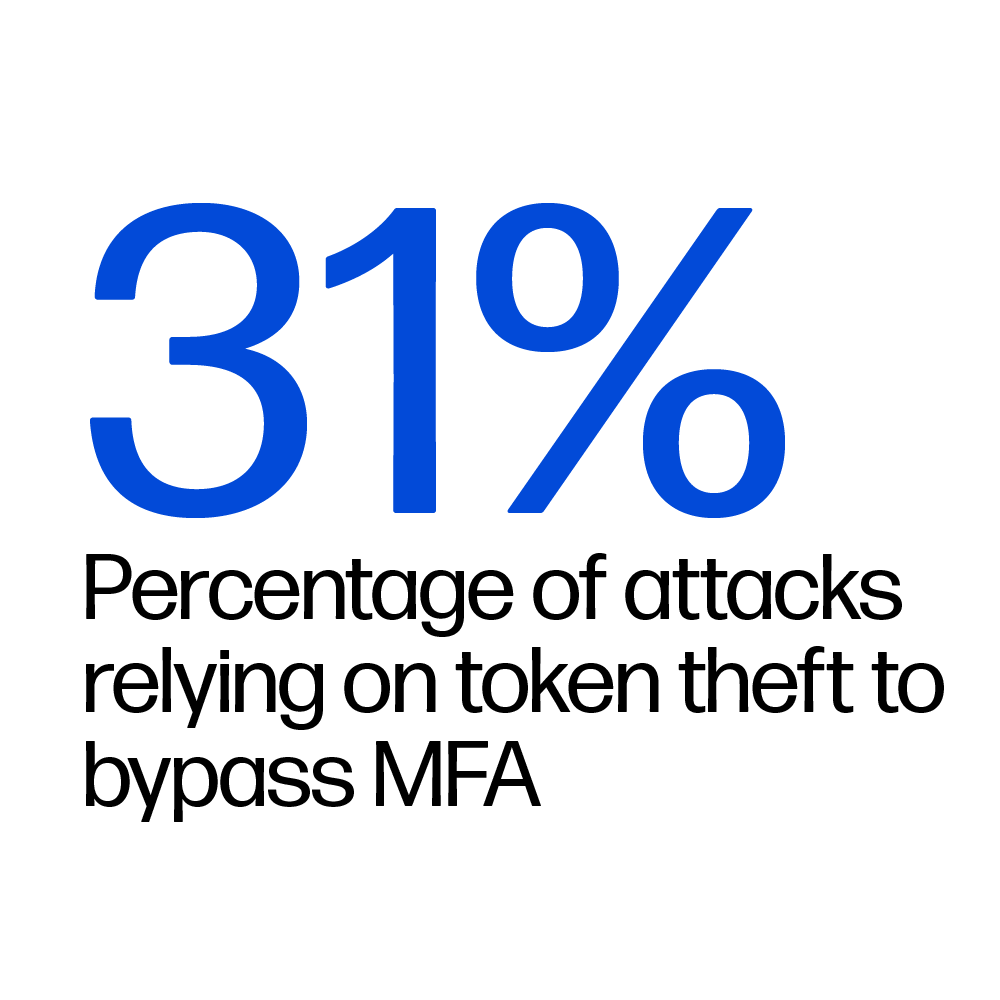
Since the user is already authenticated and the attacker has merely taken over the active session, MFA doesn’t offer protection here. In fact, of documented incidents, token theft (31%) was the most seen technique used by attackers to bypass MFA and gain access to Microsoft 365 services.[4]
A common way for threat actors to obtain session cookies is to use an information stealer. Attackers infect an endpoint with malware that is capable of either directly taking over a session and injecting commands, or exfiltrating relevant active cookies from the system to an attacker-controlled server.
The scale of information stealer usage
According to publicly reported attack data in Q3 2025, the majority of malware distributed were information stealers. Of the top 30 malware families distributed, over half (57%) were information stealers. A further 27% of the malware identified were remote access trojans (RATs), which often have session cookie-stealing capabilities.
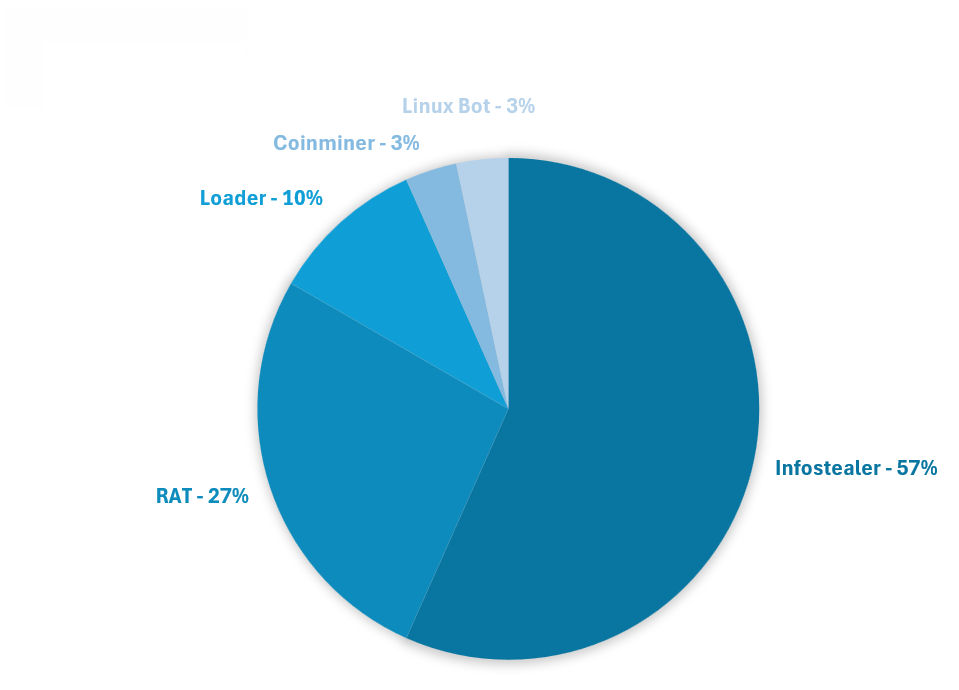
Figure 2 – Malware type distribution of samples submitted to MalwareBazaar[5] in Q3 2025
Case study: Lumma Stealer, a notable infostealer
Lumma Stealer is a malware family that is currently very active, and its scale and impact within the infostealer ecosystem is large.[6] The malware is a classic infostealer that can extract cookies from web browser sessions and exfiltrate them to a server controlled by the attacker. Between March and May 2025, Microsoft identified over 394,000 Windows computers infected globally by the malware. In mid-May, Europol and its international partners conducted a coordinated take-down operation, disrupting the malware’s infrastructure, seizing around 1,300 malicious domains that served as core components of its operations. Disruption operations often only have a temporary impact though and this was the case with Lumma Stealer.[7] Malware activity returned in July 2025, suggesting that attackers have rebuilt its infrastructure and returned to distribute the malware.
Eating cookies while they are still warm
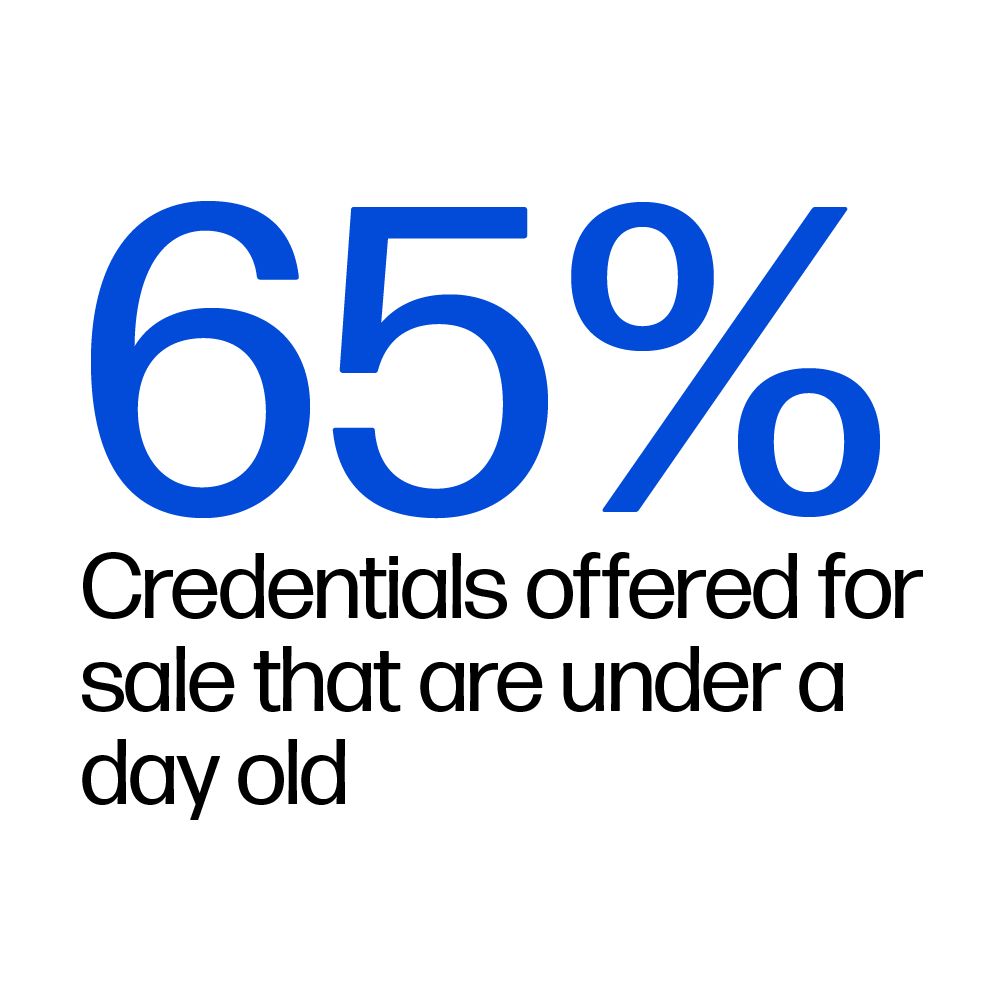
Compared to passwords, session cookies have a much shorter lifespan. Depending on the type of cookie, they have different validity periods. These range from a few hours to several days or weeks. This, however, does not mean that cookies are an unattractive target for attackers seeking to gain access to systems. On the contrary, attackers tend to act quickly and resell cookies promptly via hacking marketplaces. 65% of the credentials sold on marketplaces were advertised less than a day after they were stolen.[8]
It is therefore not surprising that such cookies are actively used in intrusions. According to Verizon, in over half (54%) of ransomware incidents analysed, the domain of the victim organization appeared first in an information stealer log or on a hacking forum.[9] Of course, this is not a direct correlation, but it does show the role of information stealers as a method for gaining initial access to systems.
Notable session cookie theft incidents
In September 2024, the Dutch national police announced that attackers had stolen contact information from various officers. The investigation into the attack revealed that the attackers gained access to their system using session cookies.[10] These had previously been stolen in an information stealer campaign and then resold via a marketplace.
In another documented case, the same method allowed attackers to gain access to sensitive systems at Electronic Arts (EA).[11] In June 2021, EA experienced a significant cybersecurity breach where hackers stole approximately 780 GB of data, including the source code for FIFA 21 and the Frostbite engine – EA’s proprietary game engine used in titles like Battlefield, Star Wars: Squadrons, and Anthem. Malicious actors purchased stolen authentication cookies advertised online for $10 USD on a dark web marketplace called Genesis. They then used the authentication cookies to hijack an already-logged-in EA employee’s account and access EA’s Slack instance. They then tricked IT support staff into granting them access to the company’s internal network.
Incidents such as these highlight how important it is for enterprises to protect themselves against session cookie theft.
Cookie theft mitigations
There are steps that organizations can take to protect against session cookie theft attacks. Attacks on cookies divide into two types:
- Theft of session cookies, which are then resold.
- Direct use of a session cookie on the infected device through command injection.
Depending on the scenario, different security measures are required. In the first scenario of cookie exfiltration and resale, organizations have several options:
- Bind the active session to a specific context. This means that the active session is only permitted in the defined context and thus remains valid. The context can be the user’s device, IP address, user agent, or even their geolocation. This prevents a stolen session cookie from being used on another device, limiting the attack.
- Reduce the session lifetime to a minimum. This means invalidating the cookie after a defined period and user inactivity, requiring the user to re-authenticate when returning to the system. Of course, this increases user friction, but it also reduces the likelihood that a cookie can be stolen and reused.
- Sensitive actions should require re-authentication. Specifically, require re-authentication for certain actions, such as adding a new administrator, changing passwords, or accessing particularly sensitive data. This means that the user must log back into the system with their password and second factor to access the relevant functionality or data. This limits the attacker’s ability to use the stolen session cookie for malicious objectives.
But where the attacker has compromised the endpoint and injects commands directly using their access, the above measures are no longer effective because the attacker already has control over endpoint accessing the privileged system. Here, one of the technologies that can help is hardware-enforced application isolation.
Protecting against cookie theft with application isolation
Even if the PC is compromised, it’s possible to protect against session cookie theft by using solutions like HP Sure Access Enterprise that apply robust application isolation on the endpoint.[12] This means isolating access to privileged applications or sensitive data from the rest of the device. Doing so prevents attackers from being able to exfiltrate cookies or use them interactively on the infected system through command injection.
Hardware-enforced application isolation achieves the strong separation of privileges that would otherwise only be possible by using separate devices, such as PAWs. In practice, organizations benefit from the privilege separation of a PAW solution, without the pain points that come with using multiple devices – namely, being costly and difficult to manage. Sure Access Enterprise is designed for privileged access scenarios and workflows, for example, supporting conditional access and a client certificate to enforce its use for access to sensitive resources.
For many years HP has been investing in hardware-enforced application isolation that isolates critical applications and data away from the rest of the system. Sure Access Enterprise opens privileged applications in micro virtual machines, completely isolating them from the host system. Nevertheless, users can still interact with the application comfortably, as if it was a native application running on the host. This allows users to manage Microsoft Entra without any worries or even make online payments without the fear of attackers taking over the active session.
Conclusion
Session cookie theft has become a serious threat for enterprises. The move to hybrid work and browser-based administration has widened the attack surface, giving threat actors new ways to hijack privileged services without touching passwords or MFA. Measures like context binding, shorter session lifetimes, and re-authentication help, but they do not close the gap when an endpoint is compromised.
Defenders need to assume breach. Protecting mission-critical applications and data requires controls that work even when malware is present. Hardware-enforced application isolation delivers that guarantee by separating sensitive workflows from the host, eliminating the path from attacker to session.
References
[1] 2025 HP Work Relationship Index
[2] 2025 Verizon Data Breach Investigation Report, p. 52
[3] 2024 Verizon Data Breach Investigation Report, p. 44
[4] 2025 Verizon Data Breach Investigation Report, p. 47
[5] MalwareBazaar – Abuse.ch
[6] Lumma Stealer, Software S1213, MITRE ATT&CK – MITRE Corporation
[7] Europol and Microsoft disrupt world’s largest infostealer Lumma – Europol
[8] 2024 Verizon Data Breach Investigation Report, p. 45
[9] 2025 Verizon Data Breach Investigation Report, p. 57
[10] AIVD and MIVD identify new Russian cyber threat actor – AIVD, May 2025
[11] Review of the Attacks Associated with Lapsus$ and Related Threat Groups – CISA, July 2023
[12] Sure Access Enterprise for Privileged Access Workstations – HP