Phishing Campaign Abuses QR Codes to Steal Credit Card Details
The festive shopping season is in full swing. This period tends to see more spam as threat actors attempt to phish credentials and credit card details. You might receive a message about a delayed package that requires you to pay a customs charge to ensure its safe delivery. Or an email from your bank alerting you to suspicious activity that asks you to log into their online portal. These common phishing scenarios are known the world over. However, we also see phishing campaigns that differ significantly based on the targeted region, language and culture. In this article, we highlight a curious Chinese-language phishing campaign that abuses QR codes to steal credit card details and other sensitive information.
An unusual document containing a QR code
Every day we track and analyze malware campaigns in our threat data. But we need to use a systematic approach to find the most notable attacks in this vast store of telemetry. One process we use is analyzing Office documents based on their visual similarity. On 25 November, we spotted a campaign that distributed Office documents through email. Notably, the documents did not contain any exploit or macro code that could execute malicious code. Instead, the documents only contained Chinese text and a QR code. We suspected the attackers might be trying to distribute mobile malware by forcing the recipients of these documents to switch to mobile devices to access malicious content. So, we set about analyzing the campaign.
 Figure 1 – Phishing document containing the QR code.
How the campaign works
First, the attackers send the document with the QR code to targets as email attachments. The document claims recipients are entitled to a government grant for the fourth quarter of 2022 based on a decision made by the Chinese Ministry of Finance and other state institutions. The document emphasizes that the notice had been communicated the previous week to build a sense of urgency, urging recipients to act quickly. Various state institutions, copyrights and security numbers are also mentioned to bolster the document’s credibility. So far, the lure meets all the classic elements of a good phishing lure: relying on authority, urgency and offering a financial incentive for taking action.
To receive the grant, the recipient is asked to scan the QR code using WeChat, a popular instant messaging, social media and mobile payment app, and then follow the instructions on the website. Using QR codes is an unusual but effective way to force the target to switch from a computer to a mobile device, which may be protected by weaker phishing protection and detection mechanisms.
When the recipient scans the QR code, they are first taken to a webpage containing the same information as in the Word document. Clicking a button enables the user to start the application for the grant. Next, the website asks for a bank card number. In the input field, there is a note that bank cards from the Industrial and Commercial Bank of China would be given priority. This notice suggests the attackers are primarily interested in such bank cards.
 Figure 2 – Information about the grant and input form for a credit card number.
After successfully entering the card number, another form appears. At this point, the attacker requests further information about the target, their bank card and credit balance. In the simplest case of credit card phishing, only the card details are collected, which can then be reused to make fraudulent transactions. Since the attackers request the target’s ID number, credit limit and current balance, this suggests they need this information to circumvent fraud detection mechanisms, or they may use the extra information for other types of identity theft. Once the target completes the form, they are shown a page with a loading icon.
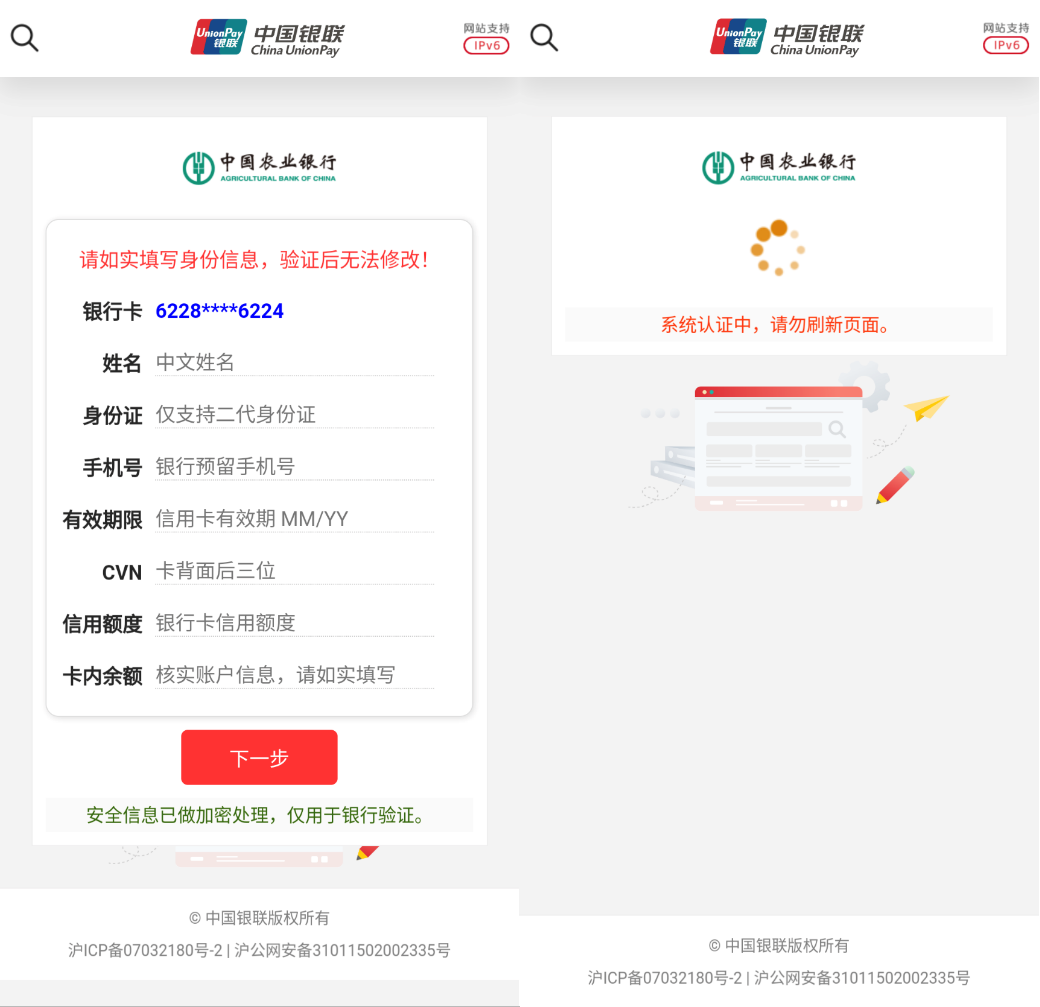 Figure 3 – Form for detailed credit card information and ID card number.
It’s unclear whether the phishing website makes a fraudulent transaction in the background or if the data is simply forwarded to the attacker. Regardless, the attacker now has all the information necessary to make fraudulent payments and can do so whenever desired.
Technical analysis
Using mobile devices to facilitate phishing is a classic attack scenario. Technically, however, the attackers implemented the campaign using modern technologies. The rendering of the page is done on the client side, and primarily only JSON messages are exchanged via a REST API. Based on the number of campaigns we have seen recently we think scalability played a role in this technology decision.
If we scan the QR code, we get the landing domain. Here we want to analyze the response of this first domain in more detail. The request returns an HTML document containing lots of encoded JavaScript code. Interestingly, the “to-data” attribute, which is set on the outermost div element, seems to contain encoded or encrypted text.
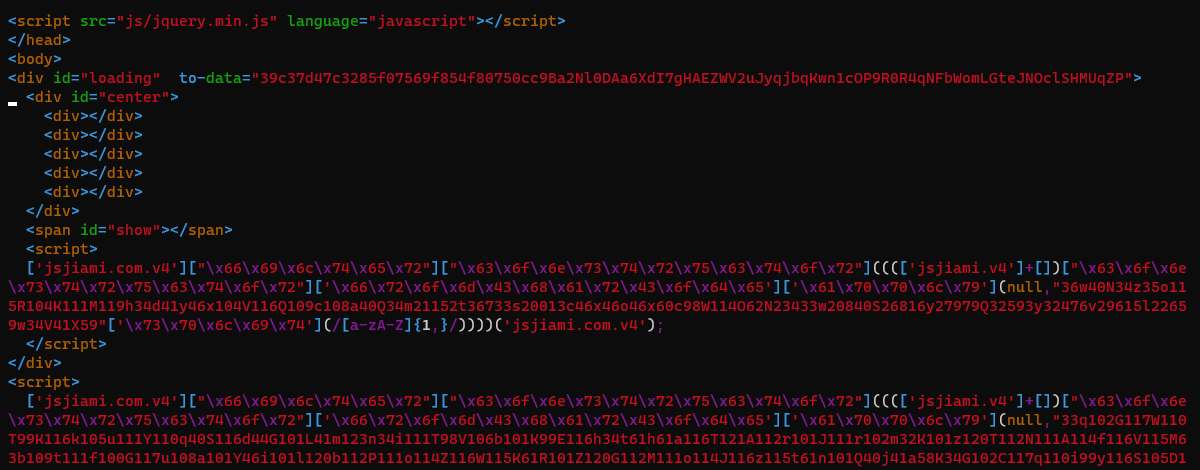 Figure 4 – Obfuscated JavaScript code.
Deobfuscating the encoded parts reveals the script’s functionality. The first encoded statement is a simple message output, where the message indicates the content being loaded. The second statement is much larger compared to the first one and decodes to JavaScript code.
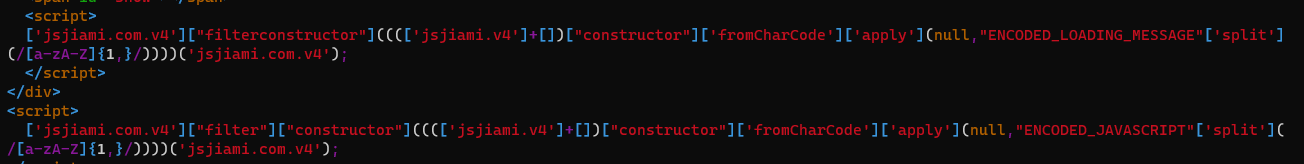 Figure 5 – Deobfuscated JavaScript code.
Now let’s take a closer look at this code. The JavaScript code is not obfuscated in this case but minimized. The idea of minimizing is not to make it harder to analyze but to reduce its size so the script loads faster in a web browser. We can reformat the script with online tools to get a more readable output for further analysis.
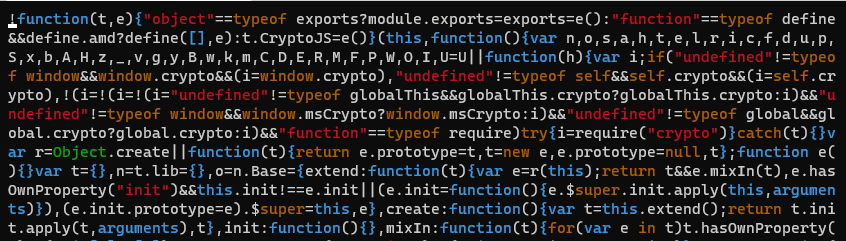 Figure 6 – Minimized JavaScript CryptoJS library.
At the very end of the script is the interesting code. The previously selected “to-data” attribute is read into a variable which is then passed to a decryption function. For decryption, the AES algorithm is used, which is implemented in the CryptoJS code library. This library is not imported as a file but is located directly in the upper area of the minimized JavaScript code. The first 16 characters of the “to-data” attribute are used as the key, the second 16 for the initialization vector, and the remaining 32 are the ciphertext.
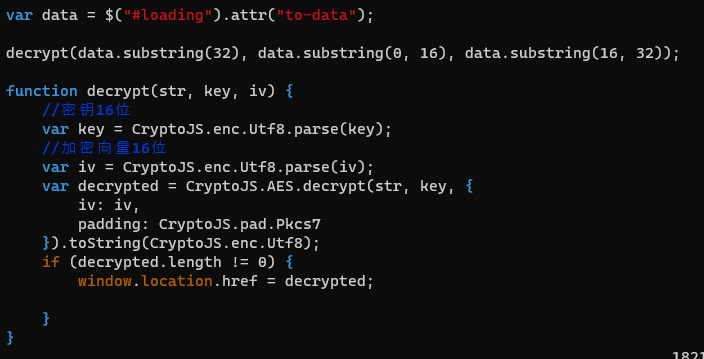 Figure 7 – JavaScript decryption function.
If the decryption is successful, this results in a new URL where the user is forwarded.
Next, we receive new HTML and JavaScript code from the forwarded domain. In this case, not only is a file loaded but so are other JavaScript files that are referenced in an index file. Some of these are configuration files for the API, functions that read cookies, or check whether the page was requested from a PC.
 Figure 8 – HTML importing various JavaScript files.
One of the functions checks whether the page was requested from a mobile device, such as a smartphone or tablet. The function determines this based on the screen size and user agent, which are provided as a request header. If specific keywords are found in the user agent, the script assumes the page was requested from a mobile device and continues execution. If this is not the case, the screen size is checked. If the screen resolution is too large, the script assumes the device is a PC and shows the target a warning message that the page can only be viewed on a mobile device. This way, the attackers ensure the target continues the phishing process on a mobile device rather than on a PC.
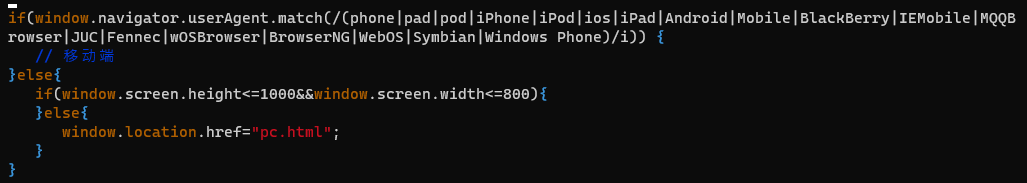 Figure 9 – JavaScript function to distinguish the device type.
The index file itself contains additional JavaScript code that is responsible for the communication with the API. The AJAX function makes a POST request to the domain defined in the configuration file and the URL path specified in the script. Since nothing is specified in the configuration file, the current domain is used. No content data is appended to the POST request, and the desired data type is set to JSON.
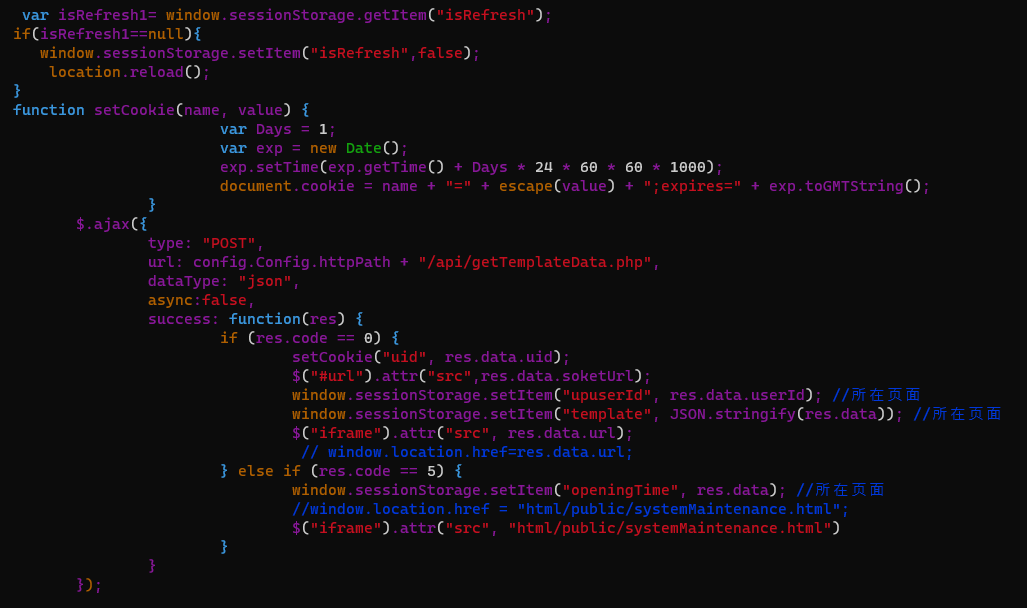 Figure 10 – JavaScript code which makes a POST request using AJAX.
If the status code of the message is 0, a UID generated by the server is set as a cookie. Subsequently, the URL in the JSON response is set as the source address of the iframe, which controls the content. A response with status code 0 is only returned if the checks were evaluated successfully and the campaign has already been activated by the attackers. In some cases, we observed that the campaign was not activated immediately and a message was displayed to the user to try again at the mentioned time. The following image shows a sample response from an active campaign.
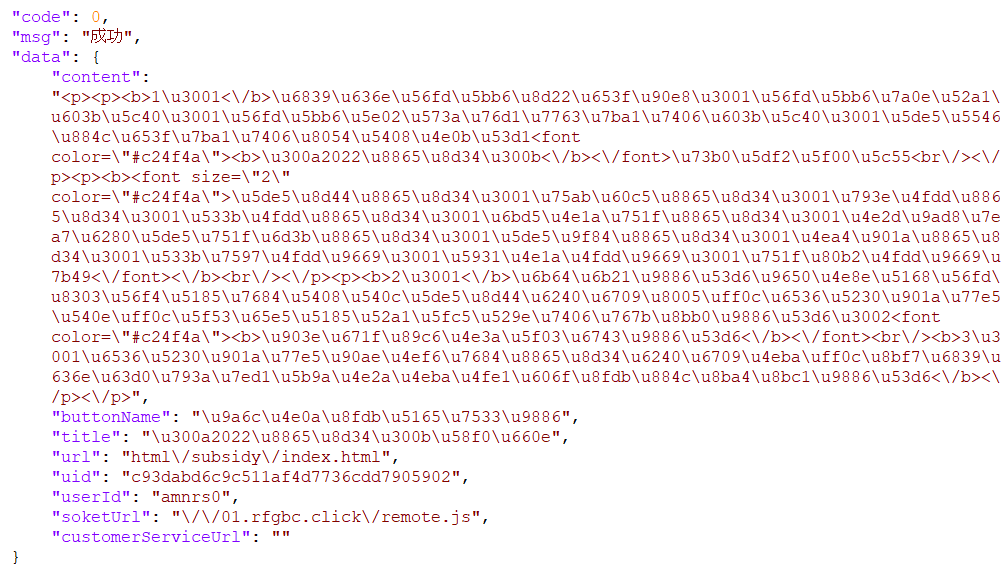 Figure 11 – JSON response from the phishing server.
In subsequent steps, JSON objects are mostly exchanged using the method we described.
Conclusion
Since the end of October, we have observed these phishing campaigns almost daily at a high cadence. We have also noticed the attackers varying the document lures and domains every day. While we cannot make conclusive statements about the size of these campaigns, the attacker’s choice of a dynamic phishing framework indicates that scalability was a consideration. Therefore, it is plausible that these campaigns are being distributed in high volumes. The structure of the phishing kit makes the content and the theme of a campaign easily interchangeable, which means the attackers can quickly switch between different lures.
These campaigns are unusual because the attackers use QR codes to force their targets to switch to mobile devices to input their details. Sending targets a document with a QR code they must scan may seem overly complex and, therefore, unlikely to generate a high participation rate. But given the popularity of making mobile payments using QR codes in China, this attack vector can be effective. Mobile devices also usually lack the same protection against phishing websites as PCs, so the device switch technique is clever way of circumventing endpoint and network protection.
Indicators of Compromise
YARA rule:
rule beian_cc_phish : maldoc image
{
    meta:
        description = "Beian QR code phishing campaign"
        author = "@stoerchl"
        date = "2022-11-28"

    strings:
        $png_img_value_0 = {89504e470d0a1a0a0000000d494844520000000e0000000e08060000001f482dd10000001974455874536f6674776172650041646f626520496d616765526561647971c9653c0000032169545874584d4c3a636f6d2e}
        $word_content = "word/document.xml"

    condition:
        all of them and uint32be(0) == 0x504b0304
}
Document hashes:
SHA256 First seen
bd606f93c1884e8def6ec232c3ceb9e827357f50831c7e9e684c581efa8a2738 2022-10-11T03:43:32
8fe2e56054140a2e82367a52d531788e79f88092c7bd1a1479bdd56c681dcc93 2022-10-27T18:30:25
91315bbbdaf6ac70af039e1577eab14206c3eb2fe9378c665818ad118caff5d2 2022-10-28T15:20:33
0d8fc3db0297f6a412dc34a85ef5eb4e108e3d0bf06a07020381bf3dbd2033da 2022-10-28T16:59:17
4faa98886bdc083a569e6ed5df34ffc994ce2d0b27a123cb89f3acecdb3b4ff5 2022-10-30T15:10:21
5dda57cb607dea66fcedeafa1ad49ecbf3da6c13005ceb6fac20be8a940a8c55 2022-10-30T15:54:42
f3229ef4481741e1fc5f211cf310b18313d7ecf267d47e07324953ecb2008bbd 2022-10-30T20:28:28
35335c5a11502faab5a62a2feca9a1d6f014aad87034b1062073e75da4181adf 2022-10-31T00:31:30
8cd6e370952c6d29a55dbd8a7ca94ca64ae738f1a301607dfef1a7d81d109fdc 2022-10-31T02:46:54
7c4b771ac185101d0869f348a3e6364a21d7580fba8f92f813ae06541d5f387c 2022-10-31T02:49:49
dfc7b0222d0549542c08e22ea60026b5c3e7b18a686984ff97486d58d1396ecf 2022-10-31T16:22:34
24e557d0fbc40f9c59e161d57c6e07e9f86fa85422a55cf7921b9c42f2d02314 2022-10-31T16:54:55
2377d7b8ce969adca48919bb96c166d4f3a4511283a99d827a5077a29e62d2cf 2022-11-01T15:21:02
b4dfe8c669f2eeaf0ac7a5f3422bd246f093b2c5446111e4dcc324424f54a273 2022-11-01T16:33:39
f8171e99ae35e6d8c6bd0d155453b1aa2d82fae394ff85882e9d205e119651d8 2022-11-01T16:53:57
b14c395ca20c404903980fe7c31fb8cbe42543b5f733b508a170ac2c8243f2a4 2022-11-01T18:20:51
5b48d9875ba4cf7b375558422062ada6c399cee6a9d234fad37bd00484a54890 2022-11-01T19:44:35
6e64cff8624cc12d91055e6d42f2a098cda7abd9d34bee5d2d113b3f20913473 2022-11-02T18:41:43
f7270defa0408aa424caa91df4533fbcfbfbfcd16a362394cb45efa54db97be0 2022-11-02T20:19:58
006a5c083edbe683ed7db74d1bb7f8ef23543d4194c107768722e38ce9ae79e3 2022-11-03T00:57:30
939656a000b7ca2f54bc42d635537261ce5194e2041f1c3ac37e3c72f8ec5333 2022-11-03T16:33:58
22df01db04ab89db7ee2ff3a97b6587137b201e52cb8b47341aec0b201c06a66 2022-11-03T16:46:14
92ee97740c9ce989dbf02f024f5330f6bb693dbf1c803c4170b24ba9255fb4cc 2022-11-03T17:23:54
00b09d701bf4f6b27eb5e98823e14199a8174fb7dfb65c6a991dd3579c4edf96 2022-11-05T06:49:38
73dbe14a8acdc5ab25f68f4952e5b9e6cc3952e57415763b699b61f3c2002431 2022-11-05T06:49:57
b6044ae0562c6a1e9de16eb4d676037ed1b632c87af30e6988218d9709cee158 2022-11-05T07:00:03
d0db84f72cb41e92dd0b0573222aa2b1189a91e228263dbd9d18d0aa906b4d53 2022-11-05T07:21:27
06b531de56900e03d5324fc014da155ae0a84366bdf6b3a7c65d0f8881fd32f2 2022-11-06T16:25:25
87bb0a8c73550aa1803c8fb44b7b16a37b641263118497cbeb05e43f27e7eeb6 2022-11-06T19:53:45
361ab7fa236bb9607d4a76a4faf35a4297d3fc15431c064ed3337f9236eea77a 2022-11-06T20:51:23
2382d0d9947403b56290da38ee91e27a55bfab1a9e5e13ab9064cf911fa2ea64 2022-11-06T20:58:35
b9e48a5eeb49d979c51f507e71f50a475869c9d3e090f10d296176a3297ca7ff 2022-11-06T21:01:06
96d2bdb350de5458156bd4f7045f440101c6fbeacfa14ef4b14e04645ebdbb1f 2022-11-07T20:16:02
c6a3cb09b84a5f0a9ad4a3d93efbab9343c21b6dec3dacca9b700c33faa8b8c6 2022-11-07T23:30:10
3d29d5e55d1b88ec610f5d390c94ff9a0c5a2c73a0256acb5cbc5d149bb76f93 2022-11-08T16:05:43
2726038d10aea149b5f386b83359664eed43cf3d376220b3f75e70997d663a38 2022-11-08T16:20:40
675b8f0223483d0f68ad8fd5fc20d9051885b491b0619de01d6ea5903799292c 2022-11-09T01:20:55
f7392d1fd89f444afed61136fdfff7212e1ce3025c817b339216e6cd520d2743 2022-11-09T05:48:43
927f90227d8321ba7de0845ef8571cd635728ec56352a9e60a9a846dfb9157fb 2022-11-09T15:12:08
1f275a6e4395ab4ddcaa1d09018dd20c994b79f7aa121b0e4f766c64291e5885 2022-11-09T16:04:23
7b4695d9efdc6f1923b9afbc07d6b784408bdef635c093085597c846372bfb9e 2022-11-09T16:09:44
743ae1aaa47c35758893f64020f57c5c29bbb67e20155d0872ee1208cbd71015 2022-11-09T17:25:55
77d0c5a8420aef92f591814009d6b5afbacf3e16c4f16f1e9c59acf6f36d3dbc 2022-11-09T19:45:03
31a63c2d926408b753edbf741cdad9b591ddc0e6a3711bd1ac361110611fac39 2022-11-10T03:16:30
3296421c9c5a21e44a76e57c07300a8886cbd0e8dd23bfa061cb0bdb60835a58 2022-11-10T03:22:37
978144376be441b4809418f93c9fd8bcc9714c3fafaadfc390fea163ac81774a 2022-11-10T13:28:58
e8f5111048249a00bac91212cc76d7f46107f4c55f0e3ad38ac4943ad4c6689e 2022-11-10T17:10:51
e6b68ac045030f10b8716d559069fb00699059ce84f67db6ba0492f2e5a4cfa3 2022-11-11T01:00:06
212c13470d2c5612c902154848fbc937d4011c89ed2b2fe40c0e64219c3f9e64 2022-11-11T19:00:39
3998cf466851f8d9f4d845049d3715506e9b1a9963412c68c5e8d8edff355654 2022-11-11T23:12:07
d08ded744bf15b273c70b2e9337c00a1ed15a5a076e7b9d4fde73ebd72f190fd 2022-11-13T15:26:55
42e90795745e7023c3a192fce1b602ad20eda349c6a2c715b29bd0150ef30289 2022-11-13T17:06:23
27c7a11e6c30c9933dd637ebeaadd6982f96d11d3097d9988e78267ba9043dbc 2022-11-13T17:38:34
89aad45732ca34dde83d3f7f436757d6c855bfad1b4a38e2ff098697016b4b60 2022-11-13T17:52:23
17b578facf7919465aaa2b7e62baba48b1a134f1bb96f10e7f5e5786269f3c96 2022-11-13T18:30:53
0f0d837fe04985501f7f42077de1ee886fe7a14385707a9a52941c748f6d3d44 2022-11-14T17:12:43
420eacf2685dbc3a831e03fcf2a4beb65653881527784ba37a3073c1a05baa29 2022-11-14T17:15:36
435959ca0026294447f72c2eb9c0c557082f24dee4fee964f9f083b3f37f785d 2022-11-14T18:28:17
4b473ce68eca6046b551ccdb676aff4431c130c20219688a7465c531772d1e69 2022-11-14T21:11:45
763c4cd1063821a0df54ac7aa871d02391716a61f48d0453b8e61a6dd1b741d7 2022-11-15T16:39:55
23fc2325fd2ef47a42078210e27cfd681a55edfc85d34a6a7bf53b9aa37d8e99 2022-11-15T17:10:44
0c8f8eff0cb7952edc32d36a28bfcda536e0370d5e1b217d36bbf081e6e567f6 2022-11-15T17:25:20
8c5865b5ac59d6a08341eb68dac221d0fc1f128b176b997b516c0c6fb861f74e 2022-11-15T17:31:28
cb8314282c863dfb948c23cc8f7c9e1b73b44368497f7463a6a3d3116ac3c829 2022-11-15T20:54:11
f130fdeaa81b3ab2bcf2397f791dc732f3b4b19e81365b1e1ac4f7ea55137ad0 2022-11-16T00:19:08
b4c2ce3511dbdacfea60d6ded52f52cab8b7aa8e58bd72557d83d35d94e02aa1 2022-11-16T13:15:52
bbe60e5bf60950f906b05a61846c81385240bf6c5ea167e757403c6554634da1 2022-11-16T15:33:45
354786dd275f9c29bf7dae5f248b13a40b411a03d2b3d832a426e6dbe49d8187 2022-11-16T16:36:17
95812b220463c364f828b7349a4a1f9353e0a334f7f06e517c71607cd9cbe187 2022-11-16T20:32:39
a34c703d9091eb02599c248a7de51332790c194a60659b686767a4bc6f59b640 2022-11-17T00:32:51
63b2fa5857a29dc1c883a6c01b5a2e7f44c6adf115d8cad512dd21b4c4227b3f 2022-11-17T01:54:27
e00a53f6a35654a2985f31c3a2ea34c28ea4ab43df92f5a2b4b4c70ec6a92a49 2022-11-17T14:33:22
737093bd17966472e506b4eef3bd1ca43ad0981aed0434d12977fc619c3389c4 2022-11-17T15:21:03
c922919d6dca27d4871c0e3f813e3080f8908e4c88f5c61a31646ae4ba4694fb 2022-11-17T17:14:41
2201d54f6f98a60b67622df4161f16d67a654b2c4be2999f9d659ef6b48d5131 2022-11-17T18:31:04
9206912713f7508dac9fc297b36894a9026b30afc9c5e59a39126f2673f0094b 2022-11-18T00:38:36
8574f9460ebf7d6f0d86d57384366f92062d4aa3cec4666b3977ce1fbbbacd26 2022-11-18T15:52:34
f71d05f77ec553dffefc1e1c297ab79cb30a3e51e4fe43b659decfcabcd8cd03 2022-11-18T16:29:44
5cb7e566a374d0bfcc5fead0e688c510addbe4f16f98e3df64c5664227ff47d7 2022-11-18T17:01:11
256c03ca22e7f21741eb6873d7ec3d5785644761b0618a374f2d95a9b91283e9 2022-11-18T18:41:12
ae8c66fbe9fcda03ea1309288ea817f930dddcaf7958fc4486fbc0fbd7c3b9d7 2022-11-20T15:39:01
46eb770a5be7d49535a2312fe946d8a8163b8f525355d1ac79d8fef3242d8319 2022-11-20T15:42:11
06b700a84ea8c98aaab5bbbcfbb6477ca5b67098b88fce97bcdd09131acd4865 2022-11-20T15:59:21
ee2bab869e06bfb75e39802695232f159fc3fe2eeca93f958bceccbb7bf0325e 2022-11-20T16:19:34
4f5a058452ec432bb2eb2e80abda44363476c1bea076d78f961d30d8b15db278 2022-11-20T17:44:21
890d0ad057fa039ee6d5073032bfdba2b5c80d15b1b57da216b8b992804e60bb 2022-11-20T18:06:54
04c8d711ae13d12199b3f8148401d2be2638102a472f4efec5e17d80e43ff9ae 2022-11-20T18:17:47
acba595f5553f7809d822c8d016f816eccd51d742b2e31fa31d0213ece0c0439 2022-11-20T20:11:31
17b1183a6fd47f6142b96d82f1ca012ceae1784cedf6d3b2019658399020e77b 2022-11-22T15:46:37
c939ae0326666b27905c943bc43cdfaf4b9e9c24991f39f703ae2752fb61b480 2022-11-22T16:07:15
fdadc18b908a145563bb375a73a09b6af87d0afecac2cceb550b80472115cfb9 2022-11-22T16:28:32
41db4919ddf1e6d66f6adee68806eb0b5461e419d998a31a4525f69a81627c8b 2022-11-22T19:29:31
a9c30e05978c0c4253c6244b599d8134e3930439097528455a6b5cbb0f544783 2022-11-23T01:24:52
549528b3d9431c481b89312abfc9b4f2aeebf4b150698a59e9d3c489c4ec44cd 2022-11-23T05:27:49
e96b7e5031f2b3cc31060f33e1352a27753eb89e7b6fd101754db9cbe21ed26c 2022-11-23T16:29:48
71d10bb7e022e6656b0df0a0031e7d979d9529707e564595a158ef4175b4fc6a 2022-11-23T16:33:30
a8f68d2548e2a5a5a53906a71c7223a52ccac7e28fa930d54d5b8f8b34b3e4c2 2022-11-23T16:50:32
eb3b0bd615f423452540dcf159a71d86cb409ed11793da70748975e5db8e2eb2 2022-11-23T18:36:30
d334fd557b3b9e4ccedcbd5f54a5c501e6540241bf1a1491f76b56dbdf8e2c9f 2022-11-23T20:11:39
077c4645d7984ed225e1fd13831bddcd18a97b63322df44ec312e4ec0993bf13 2022-11-24T15:13:59
09b50e84b3f1a4665a397e1c8d092a1fcf4170132661bfa40ccb694e1a3d392f 2022-11-24T17:29:26
8cab544e91a0e33240b89e2a167568d072da8833360d2e1be577dc44065f91f7 2022-11-24T19:49:34
9f546242ee8658083fbb9b5beac69cb8939b8a16e1d17eccb460a524a8df2e20 2022-11-25T05:32:53
aa40d060828efdcfa97f5ae41c5041fd24f5ad238e8075a0331be40bf350b5eb 2022-11-26T02:34:46
132eb84f7241e3edca677365a84bcfc01dbf19075843ad4a7a3ca12f580c265d 2022-11-27T14:42:50
d82caa1f90217dcbfb6240c070e82990dd8790af7640cb627d03dc84ccc48d1e 2022-11-27T17:56:49
29d82d6db5c26a1316ab2e7b5b59903b0d772fd96bf966ec681efa3a3b214336 2022-11-27T18:43:00
ddf5a1c09ae5a98c9fb7d94274456fc42cff7892ebdc69ec3a887977441fc6ed 2022-11-28T02:11:37
Domains:
109xyz1[.]xyz
bu11-16tie[.]xyz
butie1114[.]xyz
chinabt[.]xyz
d[.]bu03tie[.]xyz
yunding868[.]xyz
zfbutie1125[.]xyz
zhengfu-bt2022[.]xyz
bnrdx[.]fun
erhvc[.]fun
mjhyr[.]fun
rtgwe[.]fun
w[.]jytq[.]fun
w[.]nkgv[.]fun
dfhed[.]click
lkjytg[.]click
lokiuj[.]click
qwerhja[.]click
qwsax[.]click
rtyhfa[.]click
vgfwe[.]click
zswqe[.]click
ccahhjc[.]cn
czatmfk[.]cn
fjsoxqq[.]cn
gmftlon[.]cn
gnejuoj[.]cn
gwlmgfk[.]cn
ikdufzn[.]cn
jncztwc[.]cn
jtvqdpe[.]cn
khch3[.]cn
lgacjgr[.]cn
lqlgdmt[.]cn
lykcjhg[.]cn
misss[.]voto
nfldyti[.]cn
nuko[.]vip
oeyinia[.]cn
prajftk[.]cn
rzkrfhq[.]cn
tyrvhkj[.]cn
ucgwchd[.]cn
ughmadu[.]cn
vzqvqft[.]cn
wtcrmnq[.]cn
xyoiqqc[.]cn
yvgxran[.]cn
zevalcg[.]cn
zjkthet[.]cn
zrfwucv[.]cn
c[.]ofanwvh[.]cn
t[.]byijpwi[.]cn
w[.]ayafdey[.]cn
w[.]berncng[.]cn
w[.]bknwflu[.]cn
w[.]bnlnbde[.]cn
w[.]byijpwi[.]cn
w[.]cbpgoqs[.]cn
w[.]ciazquw[.]cn
w[.]dhwsixz[.]cn
w[.]fdvencb[.]cn
w[.]fgcpdfd[.]cn
w[.]fwfyhsj[.]cn
w[.]fyhmotg[.]cn
w[.]gniarug[.]cn
w[.]gogssfu[.]cn
w[.]hdtnaqv[.]cn
w[.]hidlxeu[.]cn
w[.]hxzebff[.]cn
w[.]hzhihtp[.]cn
w[.]jrhruhi[.]cn
w[.]kgpmwvq[.]cn
w[.]mqsfjdl[.]cn
w[.]mrjyvkv[.]cn
w[.]mryrej[.]cn
w[.]naptxzr[.]cn
w[.]nmajfpa[.]cn
w[.]nnmitbk[.]cn
w[.]pskbtpk[.]cn
w[.]qhvkohl[.]cn
w[.]rftbbzi[.]cn
w[.]ribxmxb[.]cn
w[.]rxueya[.]cn
w[.]tbebqjp[.]cn
w[.]tiywex[.]cn
w[.]tnqxzxi[.]cn
w[.]twuwnrw[.]cn
w[.]uakxxvs[.]cn
w[.]ufkbeow[.]cn
w[.]vrtkkjd[.]cn
w[.]vwtxqrd[.]cn
w[.]xhldapr[.]cn
w[.]xvtnuox[.]cn
w[.]ywzxzli[.]cn
w[.]zfeoqcz[.]cn
w[.]zgixlus[.]cn
e9c9d96bc358c2e32bc0611b002bee83[.]ioujsd[.]click
d37365dd85df84eb2fc6fee6a3a81370[.]iyuhng[.]click
3fb7ab2a5e5ccf51ecadc34798f16c54[.]htgjkb[.]click
116bff40875f1e6218c448e7e2c5e596[.]cvbgte[.]click